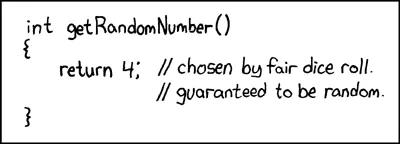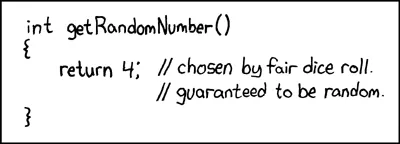
This is a good comprehensive article reviewing the security breaches there have been recently (and there have been a lot) and discussing what we should expect, and do, in the light of AI-assisted service compromises. If you're wondering why everyone was making '4' jokes recently, it's this: "eMudhra broke this trust in the most blatant way: its private keys turned out to be single-digit numbers. A private key is a 384-bit key, which means that it would be a number between 0 and 2^384, (a number with 116 digits!) Except, the key turned out to be the number '4.'" Author Gergely Orosz expects the security problems to get worse before they get better, not the least because of security handled the eMudhra way. But here's my own take: for the most part, what we're seeing are not new compromises (the PHP issue, for example, was known for quite a while beforehand), but rather, compromises by new players. Before now, you had to be a government or large company to breach security like this; now many more people can do it. As we repair these breaches (and they are being repaired, because they have to be) we reduce the ability of everyone to breach our systems, including especially the governments and companies that have been doing it all along.
Today: Total: [] [Share]